


Just because it’s a familiar tactic doesn’t mean you can let your guard down. A similar attack method using cryptocurrency rewards as bait has recently been identified again. This time, a case was confirmed in which the Node.Js-based malware JSCEAL was distributed through Facebook ads impersonating a cryptocurrency exchange. The threat actors lured users to […]
Overview AhnLab monitored APT (Advanced Persistent Threat) attacks targeting entities in Korea using its own infrastructure. This report summarizes the types and statistics on domestic APT attacks identified during the month of August 2026. Trends of APT Attacks in South Korea Most of the APT attacks detected in South Korea were distributed via spear phishing […]


Overview In the third quarter of 2026, there was a notable increase in cases where attackers attempted to establish persistence and expand their attacks using paths trusted by the organization following their initial access. Attacks on perimeter devices such as NetScaler and Cisco FMC led to the installation of web shells (server-side scripts for remote […]
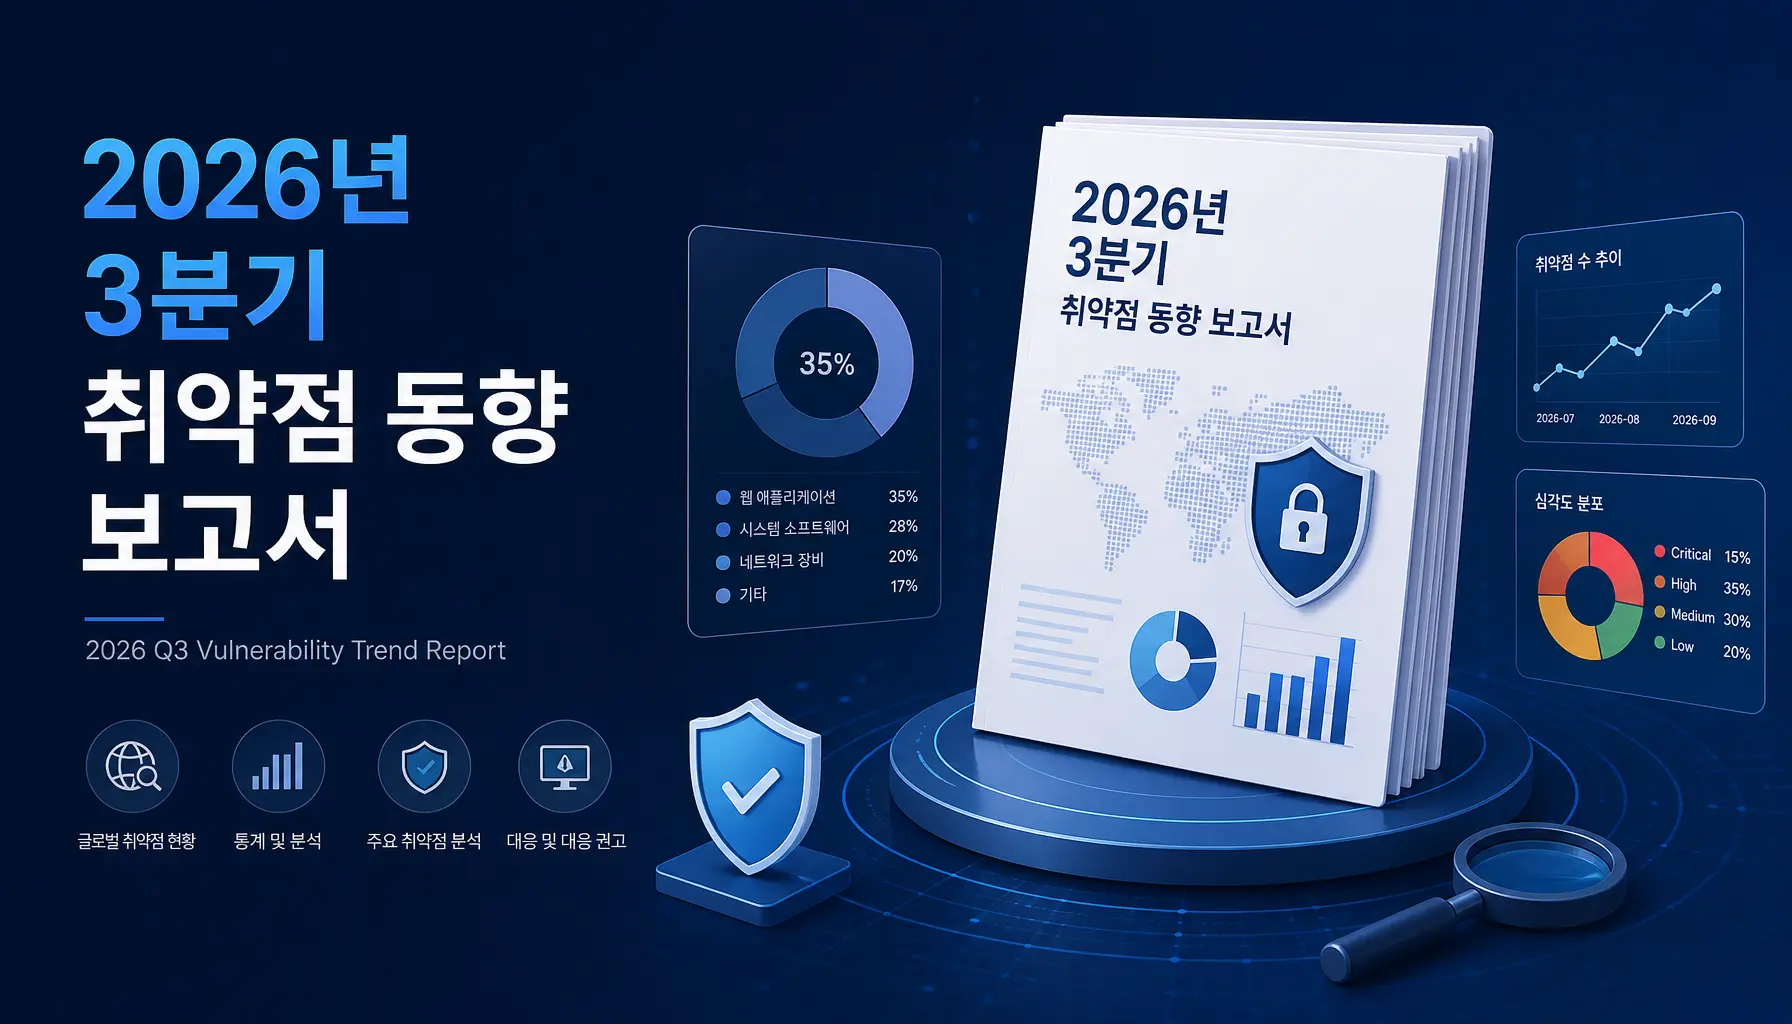
Summary of Vulnerability Trends for the Third Quarter of 2026 A total of 36,971 CVEs were disclosed in the third quarter of 2026, representing an increase of approximately 78.6% Compared to the second quarter. Among the vulnerabilities for which CVSS assessments were completed, approximately 12.7% Were rated “Critical” and approximately 42.6% Were rated “High,” meaning […]
Overview AhnLab monitored APT (Advanced Persistent Threat) attacks targeting entities in Korea using its own infrastructure. This report summarizes the types and statistics on domestic APT attacks identified during the month of August 2026. Trends of APT Attacks in South Korea Most of the APT attacks detected in South Korea were distributed via spear phishing […]
The threat actor used SEO poisoning (a technique that exploits search results to redirect users to fake sites) to distribute a malicious installer disguised as a KakaoTalk installer. The appearance and packaging method of the installer changed continuously, and the threat actor sequentially used NSIS, Advanced Installer, and Inno Setup. It contained both legitimate installation […]
Purpose and Scope This report summarizes statistics on new ransomware samples, affected systems, and statistics on targeted businesses collected during the month of August 2026, as well as major Korean & Global ransomware issues. Statistics on targeted businesses were compiled based on the time when publicly available information from ransomware groups’ DLS (Dedicated Leak Sites, […]
Content This report summarizes the distribution channels, number of Infostealers, number of detections, and companies disguised as targets by new Infostealers collected during the month of August 2026. It is based on data from AhnLab SEcurity intelligence Center (ASEC), AhnLab product diagnostic logs, automated data collection systems, email honeypot systems, and automated C2 analysis systems. […]