


Analysis of the GitHub “php2shell” Repository: Public PoCs and Defense Tools That Spread Immediately After the Disclosure of the PHP Vulnerability
Overview Immediately after the PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619 were disclosed on October 21, 2026, a large number of repositories named “php2shell” were created in a short period of time on GitHub, a code repository platform. Of the top 100 repositories (excluding forks) found by searching for “php2shell,” 99 addressed
Reproducing the PHP2Shell Vulnerability and Detection Using AhnLab EDR/XDR
On October 22, 2026, the PHP Security Team announced in an advisory that it would release security updates addressing the vulnerabilities CVE-2026-109618 and CVE-2026-109619. Although the causes of the two vulnerabilities differ, they are both remote code execution vulnerabilities that allow an unauthenticated threat actor to execute arbitrary code remotely.
“Approximately 110,000 PHP Servers” in Korea: How Were They Counted?
After an article titled “Two Critical PHP Vulnerabilities Discovered… Urgent Updates Needed Due to Risk of Web Server Attacks” was posted on the AhnLab website yesterday (October 21), we received many inquiries asking for the basis of the figure “approximately 110,000 Korean PHP server IP addresses” cited in the article.
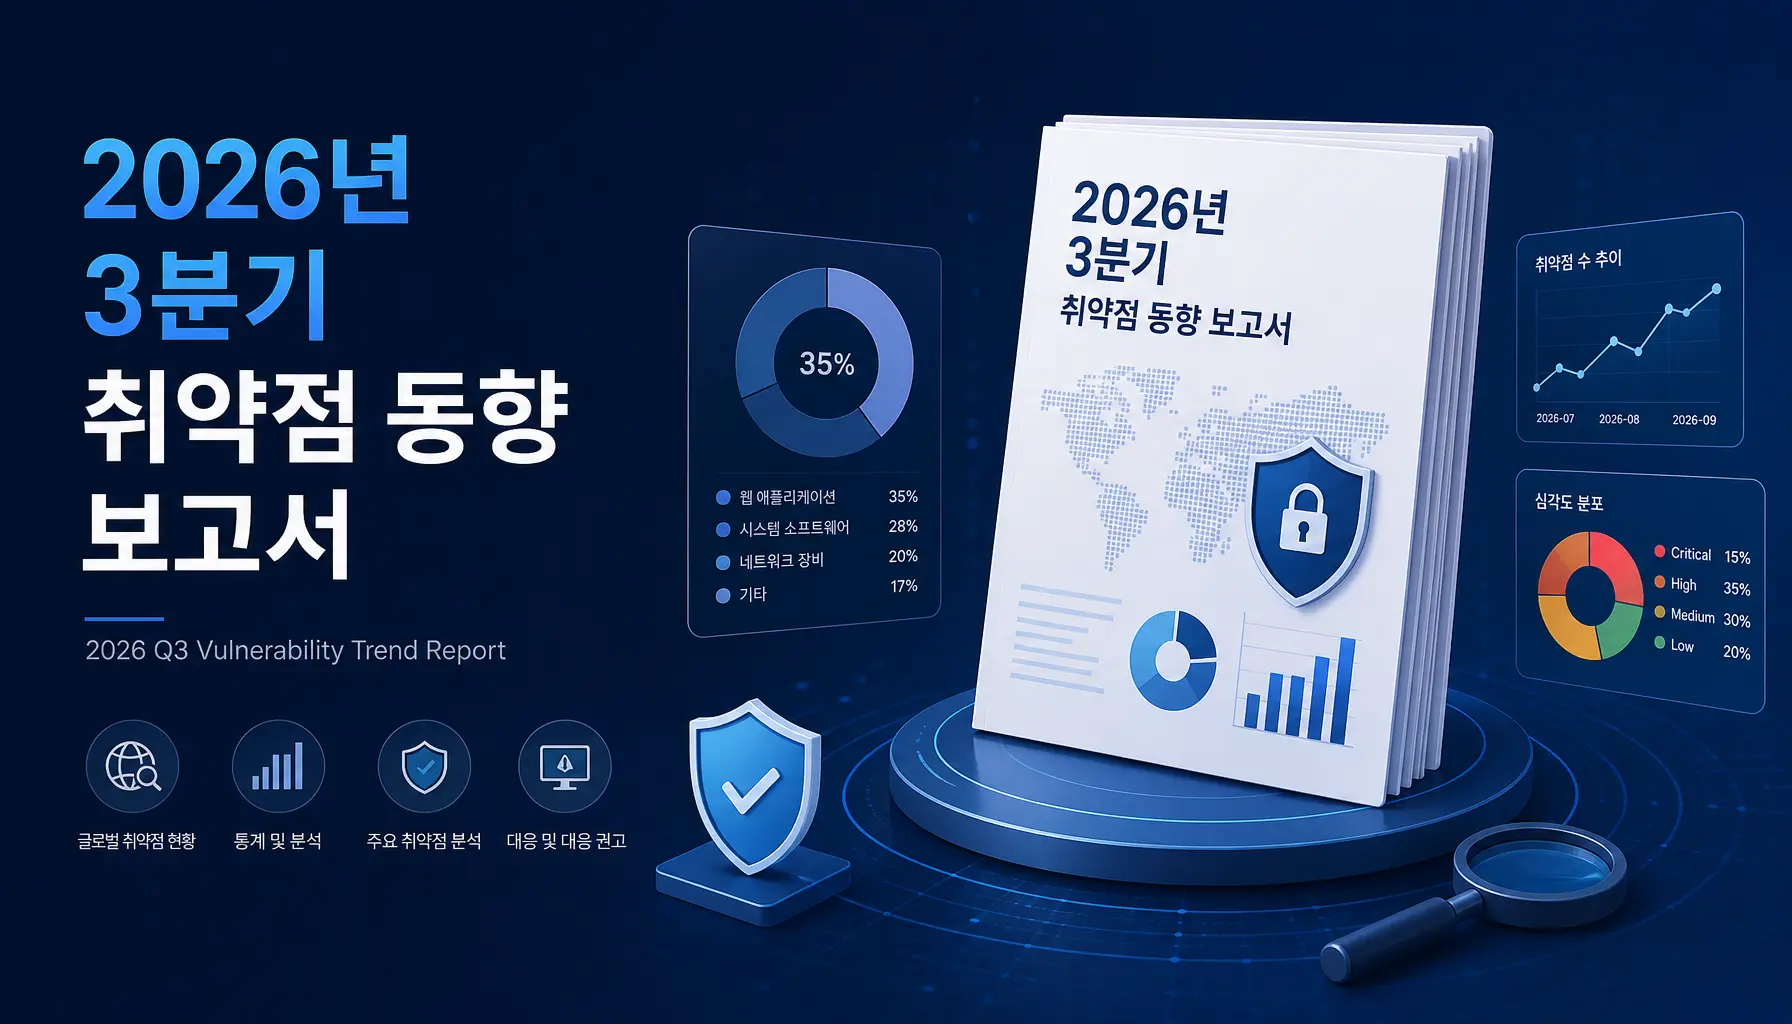
Q3 2026 Vulnerability Trend Report
Summary of Vulnerability Trends for the Third Quarter of 2026 A total of 36,971 CVEs were disclosed in the third quarter of 2026, representing an increase of approximately 78.6% Compared to the second quarter. Among the vulnerabilities for which CVSS assessments were completed, approximately 12.7% Were rated “Critical” and approximately
Vulnerability Trend Report for Q2 2026
Summary of Vulnerability Trends for the Second Quarter of 2026 A total of 20,701 new CVEs were reported in the second quarter of 2026. Of these, 2,317 were “Critical” vulnerabilities with a CVSS score of 9.0 Or higher, accounting for 11.2% Of the total. Medium- and high-risk vulnerabilities, including those
The proliferation and evolution of AI-powered hacking tools – how generative AI has changed the cyber attack ecosystem and response strategies
WormGPT, which emerged in June 2023, has brought a paradigm shift to the cybercrime ecosystem. generative AI has lowered the barrier to entry for attacks, and AI-powered hacking tools are rapidly proliferating in both paid subscription services and free open source. furthermore, AI is evolving beyond the creation of attack
Q1 2026 Vulnerability Trends Report
Vulnerability Trends Summary for Q1 2026. Overview. q1 2026 saw a number of high-risk vulnerabilities reported with either public disclosures or confirmed exploits. an increase in remote code execution and authentication bypass family vulnerabilities was observed. Early publication of PoCs accelerated threat propagation. the potential for chain attacks through the
MongoBleed (CVE-2025-14847): A Critical MongoDB Memory Leak Vulnerability Hidden for 8 Years
Overview In late 2025, a high-severity memory information disclosure vulnerability that had been lurking in MongoDB for years was finally revealed. Dubbed MongoBleed, this flaw allows unauthenticated attackers to read uninitialized heap memory, potentially exposing sensitive information. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added this vulnerability to
React2Shell: Serious RCE Vulnerability Threatening the Latest Web Frameworks (CVE-2025-55182)
Overview In December 2025, a serious security vulnerability named Reach2Shell was disclosed, shaking the web development ecosystem. This vulnerability affects applications using React Server Components and the Flight protocol, allowing threat actors to execute arbitrary code on the server with a single HTTP request. It has been given a Common
The Shadow of JWT-Based Authentication: A Fatal Threat Behind the Convenience
Overview JWT, which has become the standard for modern web applications and mobile apps, provides the convenience of stateless authentication. However, when operated and managed unsafely, it can become a single point of failure that collapses the entire authentication system. This post introduces the concept and authentication methods of JWT,

