


Ransom & Dark Web Issues Week 4, August 2025
ASEC Blog publishes Ransom & Dark Web Issues Week 4, August 2025 Qilin Targets Japanese Automotive Design Firm in Ransomware Attack Attempt to Sell South Korean Local Government Data on DarkForums Raises Credibility Concerns Emerging Ransomware Group Cephalus Hits at Least 9 Organizations, Reveals Victims via

Warning About NightSpire Ransomware Following Cases of Damage in South Korea
NightSpire operates a DLS (Dedicated Leak Site) and posts a countdown timer for the public release of information and data about victims. The group is known for using highly threatening language for their cyber extortion. This post describes the analysis and characteristics of NightSpire ransomware. 1. Overview 1.1. NightSpire

Interlock Ransomware’s Targeted Attacks on Companies
Summary About Interlock – Appeared at the end of September 2024 – Ransomware attacks targeting companies in various countries and industries worldwide – Recently, there have also been ransomware attacks in various industries such as healthcare, education, and public institutions (e.g., DaVita, Andretti Indoor Karting & Games) – Uses unclear
Underground Ransomware Targeting Korean Companies
The Underground ransomware gang is launching continuous ransomware attacks against companies in various countries and industries, including South Korea. This post describes the analysis and characteristics of the Underground ransomware. 1. Overview 1.1 Team Underground The ransomware strain operated by the group known as Underground was first identified in

Ransom & Dark Web Issues Week 3, August 2025
ASEC Blog publishes Ransom & Dark Web Issues Week 3, August 2025 WARLOCK launched a ransomware attack targeting a telecommunications provider in France. The pro-Israeli hacktivist group “313 Team” claims to have conducted DDoS attacks against nine institutions in Saudi Arabia. Qilin carried out
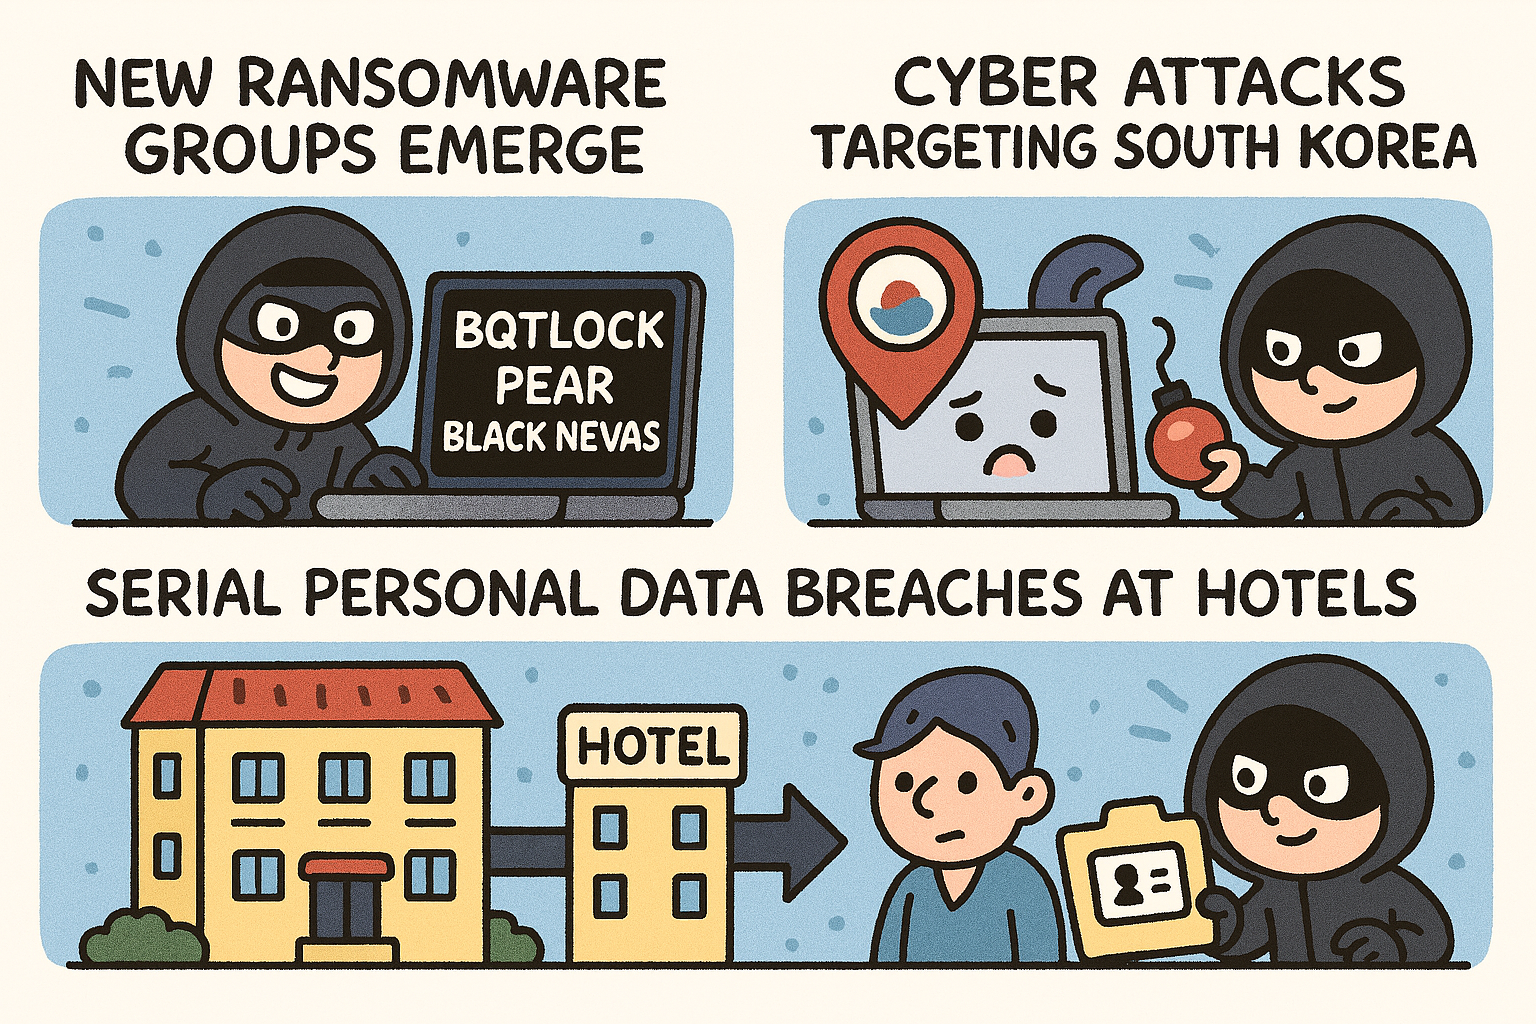
Ransom & Dark Web Issues Week 1, August 2025
ASEC Blog publishes Ransom & Dark Web Issues Week 1, August 2025 Emergence of New Ransomware Groups: BQTLock, Pear, and Black Nevas Increase in Cyberattacks Targeting South Korea [1], [2], [3] Ongoing Identity Information Leaks Targeting Hotels in Europe [1], [2], [3], [4]

July 2025 Security Issues in Korean & Global Financial Sector
This report comprehensively covers actual cyber threats and security issues that have taken place targeting financial companies in Korea and abroad. This report includes an analysis of malware and phishing cases distributed to the financial industry, the top 10 malware strains targeting the financial sector, and statistics on the industries
Makop Ransomware Identified in Attacks in South Korea
AhnLab SEcurity intelligence Center (ASEC) recently identified cases of Makop ransomware attacks targeting South Korean users. The Makop ransomware has been distributed to South Korean users by disguising as resumes or emails related to copyrights for several years. Recently, it has been reported that the ransomware is exploiting RDP for

Gunra Ransomware Emerges with New DLS
AhnLab TIP monitors the current ransomware group activities across dark web forums, marketplaces, and other sources. Through the Live View > Dark Web Watch menu, users can track the most active ransomware groups, uncover their collaborations, and gain insights into planned attacks and techniques—enabling user organizations to anticipate threats, prepare
June 2025 Threat Trend Report on Ransomware
This report provides statistics on the number of new ransomware samples and affected systems, and affected companies that were collected in June 2025, as well as major ransomware issues in and out of Korea. Below is a summary of the information. The statistics on the number of ransomware samples

