


Linux Kernel Security Update Advisory
Overview A security update has been released to address CVE-2026-31554, a vulnerability discovered in the Linux kernel. This vulnerability is a “use-after-free” vulnerability that occurs in the sysfutexrequeue() function of the futex (fast user-space mutex) component when different flags are used together. Affected Systems Linux Kernel versions 6.7 Through 6.12.80.

Statistical Report on Malware Targeting Linux SSH Servers in Q2 2026
Content In the second quarter of 2026, the AhnLab SEcurity intelligence Center (ASEC) collected and analyzed attack logs targeting poorly managed Linux SSH servers through honeypots. The scope of the analysis covers attack sources that progressed to executing actual malware installation commands, as well as statistics on the malware used
Linux Kernel Security Update Advisory (CVE-2026-31431)
Overview A security update has been released for CVE-2026-31431, a vulnerability in the Linux Kernel. the vulnerability is described as an incorrect in-place handling vulnerability in the algif_aead cryptographic interface (the interface that handles cryptographic operations). Affected by Linux Kernel versions 4.14 and later but earlier than 6.18.22. Linux Kernel
Q1 2026 Malware Statistics Report for Linux SSH Servers
Overview. ASEC analyzed the statistics of attacks against Linux SSH servers in Q1 2026 based on honeypot logs. The P2PInfect worm dominated, accounting for 70.3% of all attack sources, and DDoS bots such as Mirai, XMRig, Prometei, and CoinMiner were identified as the main threats. Purpose and Scope. the purpose
Statistics Report on Malware Targeting Linux SSH Servers in Q4 2025
AhnLab SEcurity intelligence Center (ASEC) utilizes a honeypot to respond to and classify brute-force and dictionary attacks targeting poorly managed Linux SSH servers. This post covers the status of the attack sources identified in the logs from the fourth quarter of 2025 and the statistics of attacks launched by these
Analysis of Gunra Ransomware Using Vulnerable Random Number Generation Function (Distributed for Linux Environments in ELF Format)
The Gunra ransomware group, which began its activities in April 2025, has been launching continuous attacks against various industries and companies around the world. Cases of damage have been reported in Korea as well. The distributed Gunra ransomware is available in two formats: an EXE file format for Windows environments

Analysis of Qilin Ransomware Using Selective Encryption Algorithm (Distributed Targeting Linux, ELF Type)
There has recently been a surge in the tendency for attacks targeting Korean asset and investment management companies. As described in this report, the ransomware encrypts files with an AES symmetric key and then encrypts that AES symmetric key with an RSA public key. This means that the possibility of

Statistics Report of Malware Targeting Linux SSH Servers in Q3 2025
AhnLab SEcurity intelligence Center (ASEC) is using a honeypot to respond to and categorize brute-force and dictionary attacks that target poorly managed Linux SSH servers. This post covers the status of the attack sources identified in logs from the third quarter of 2025 and the statistics of attacks performed by
Linux Kernel Security Update Advisory (CVE-2025-21692)
Overview We have released a security update to address a vulnerability in the Linux kernel. Affected product users are advised to update to the latest version. Affected Products CVE-2025-21692 Linux Kernel Version: 5.6 and later Resolved Vulnerabilities Index Overrange Vulnerability in ETS Qdisc in
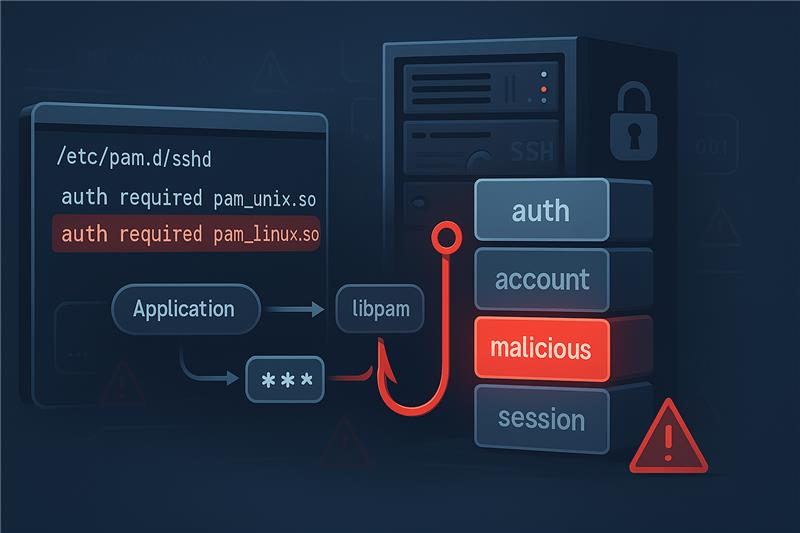
Detecting Malware Exploiting Linux PAM through AhnLab EDR
Pluggable Authentication Modules (PAM) is a modular framework that allows applications such as su, sudo, and sshd to perform security policy logic such as authentication without implementing it directly. Applications delegate authentication to the libpam library, which then loads and executes PAM modules according to the configuration information before aggregating

