


August 27, 2026
August 27, 2026 Hash 17d69eaa8df7babd5ec47cede43dc6ac7 2b7a1a3d2d3122792b5129d856f548bab 3825580057c45dd3a2dfffe20069f4065 URL 1http[:]//gdcgroup[.]vn/ 2http[:]//dennyandrewsford[.]com/ 3http[:]//biodina[.]com[.]br/ IP 180[.]94[.]92[.]28 280[.]94[.]92[.]163 336[.]163[.]100[.]194...
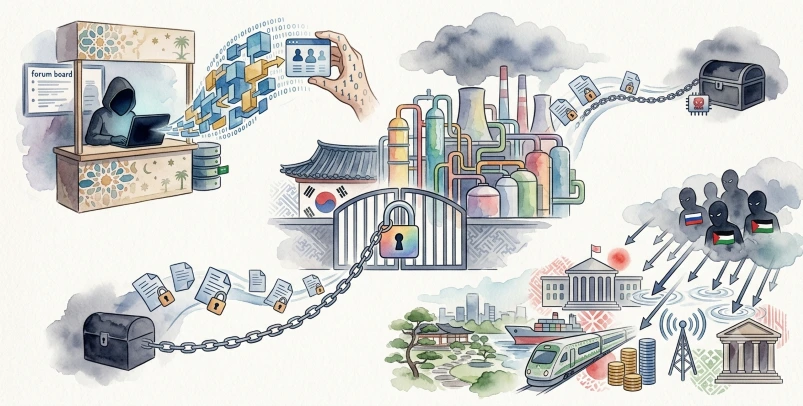
Ransom & Dark Web Issues Week 4, August 2026
ASEC Blog publishes Ransom & Dark Web Issues Week 4, August2026 Saudi Arabian Digital Entertainment Streaming Service User Data Offered for Sale SAFEPAY Ransomware Attack on a South Korean Industrial Gas Manufacturer and Supplier NoName057(16) and BD Anonymous Claim DDoS Attacks Against Major Japanese Organizations

IBM Product Security Update Advisory
Overview Security updates addressing multiple vulnerabilities in IBM products have been released. The affected products are IBM webMethods Integration (on-premises), IBM Power HMC, WebSphere Application Server – Liberty, IBM Power Systems Firmware, IBM Portieris, IBM System Storage DS8A00, and IBM DS8900F. Identified Vulnerabilities CVE-2026-12118 is a remote code execution vulnerability
Citrix Product Security Update Advisory
Overview Citrix has released security updates to address vulnerabilities in its NetScaler ADC and NetScaler Gateway products. Users of these products should update to the latest version. Affected Products NetScaler ADC and NetScaler Gateway version 13.1: 13.1 Or higher, but less than 13.1-63.18. NetScaler ADC and NetScaler Gateway version 13.1:
Langflow OSS Security Update Advisory
Overview A security update has been released to address several vulnerabilities found in Langflow OSS. Affected Versions range from Langflow OSS 1.0.0 Through 1.10.3. Identified Vulnerabilities CVE-2026-7646: Arbitrary file read vulnerability. CVE-2026-8446: Authentication bypass vulnerability. CVE-2026-9077: Bypass of the “localhost-only” restriction and arbitrary MCP server configuration creation vulnerability. CVE-2026-17623: Arbitrary
Siemens (Element Maps) Product Security Update Advisory
Siemens has released a security update to address vulnerabilities in the Element maps-ng product. The affected products are Element maps-ng versions prior to V47.12.3, Element maps-ng versions prior to V48.11.3, And Element maps-ng versions prior to V49.16.1. The vulnerability is an XSS vulnerability (a vulnerability that allows malicious scripts to

