August 2026 Threat Trend Report on Ransomware
Purpose and Scope
This report summarizes statistics on new ransomware samples, affected systems, and statistics on targeted businesses collected during the month of August 2026, as well as major Korean & Global ransomware issues. Statistics on targeted businesses were compiled based on the time when publicly available information from ransomware groups’ DLS (Dedicated Leak Sites, i.E., Ransomware PR sites or PR pages) was collected via the ATIP (AhnLab TIP, Threat Intelligence Platform) infrastructure.
Key Statistics
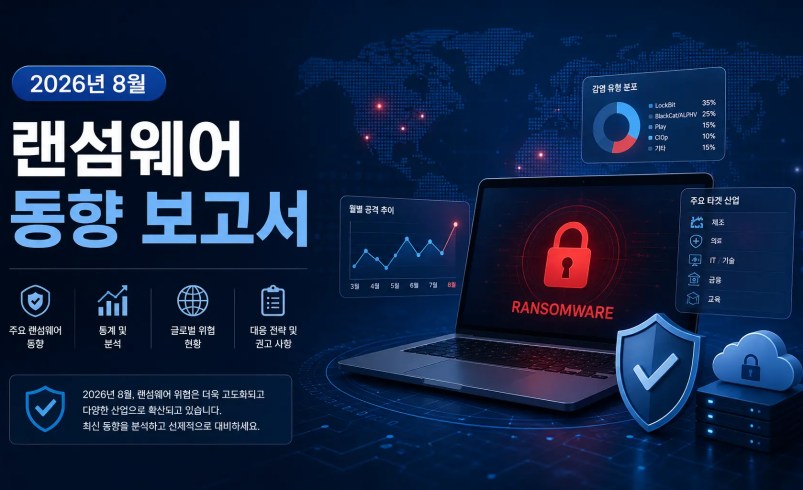
In August 2026, the Information and communication sector (63 incidents) had the highest number of affected industries, followed by Manufacturing (46 incidents) and Wholesale and distribution (26 incidents). Damage was also confirmed in Professional, scientific, and technical services (18 cases), Health and social welfare services (13 cases), and Construction (13 cases).
By affected region, the US (us) (158 cases) accounted for the overwhelming majority, followed by Cyprus (cy) (15 cases), Italy (IT) (14 cases), France (FR) (13 cases), the United Kingdom (GB) (11 cases), Canada (CA) (11 cases), Germany (DE) (10 cases), and India (IN) (10 cases). Based on the top 10 groups, Qilin ranked first with 167 cases of damage, followed by Gentlemen in second place with 112 cases of damage. Orova (43 cases of damage), DarkProject (41 incidents), Akira (40 incidents), IncRansom (39 incidents), KryBit (36 incidents), DireWolf (35 incidents), EVEREST (34 incidents), and CmdOrganization (30 incidents) followed. The total number of damage incidents among the top 10 groups was 577, an increase from 406 in the previous month.
Major Issues
In August 2026, major groups such as The Gentlemen, Qilin, CL0P (Clop), Gunra, CRPx0, DragonForce, Orova, FulcrumSec, Emperador, and Helix continued their activities. At the same time, groups such as ZaWoo, Falcon, Booba Team, Majinahanashi, VYPR, iah647, DYSPHOR1A, Moondancer, Settra, FEMBOY, Eclipse, xpl0itrs, BlueWhale, Sovcali, Dark Project, Panzer, BARRACUDA, and Storm emerged.
Qilin claimed responsibility for an attack targeting the US federal law enforcement agency, the ATF (Bureau of Alcohol, Tobacco, Firearms and Explosives), and the ATF officially confirmed that its CALEA system had been compromised. This is an example of an attack on a law enforcement agency resulting in actual damage.
CL0P (Clop) exploited vulnerabilities in PTC Windchill and FlexPLM product lifecycle management software, adding 42 companies and organizations from 33 countries worldwide to its list of victims in quick succession. The list of victims included Shell, Mindray, Continental Aerospace, and FIS Global, reaffirming the far-reaching impact of large-scale supply chain attacks.
In South Korea, Black X targeted IWIN, Emperador targeted Hanwha Renewables, SafePay targeted Air Liquide Korea, PANZER targeted DL E&C, Qilin targeted HIGEN MOTOR, DragonForce targeted EduSpa, Gunra targeted World Tube, and BARRACUDA launched attacks against four organizations based in South Korea and the US.
Conclusion
In August 2026, the ransomware threat landscape exhibited a complex pattern characterized by both multinational attacks by established major groups and the continuous emergence of new groups. By industry, damage was particularly pronounced in the Manufacturing sector, information and communication (ICT) sector, public and law enforcement sectors, and finance; by region, widespread damage was confirmed, centered on the US. Continuous monitoring is now essential to prepare for the spread of new groups and large-scale campaigns exploiting vulnerabilities.